
Data Centers
AI vs. the Manhattan Project: Why the Comparison Breaks Down in 2026

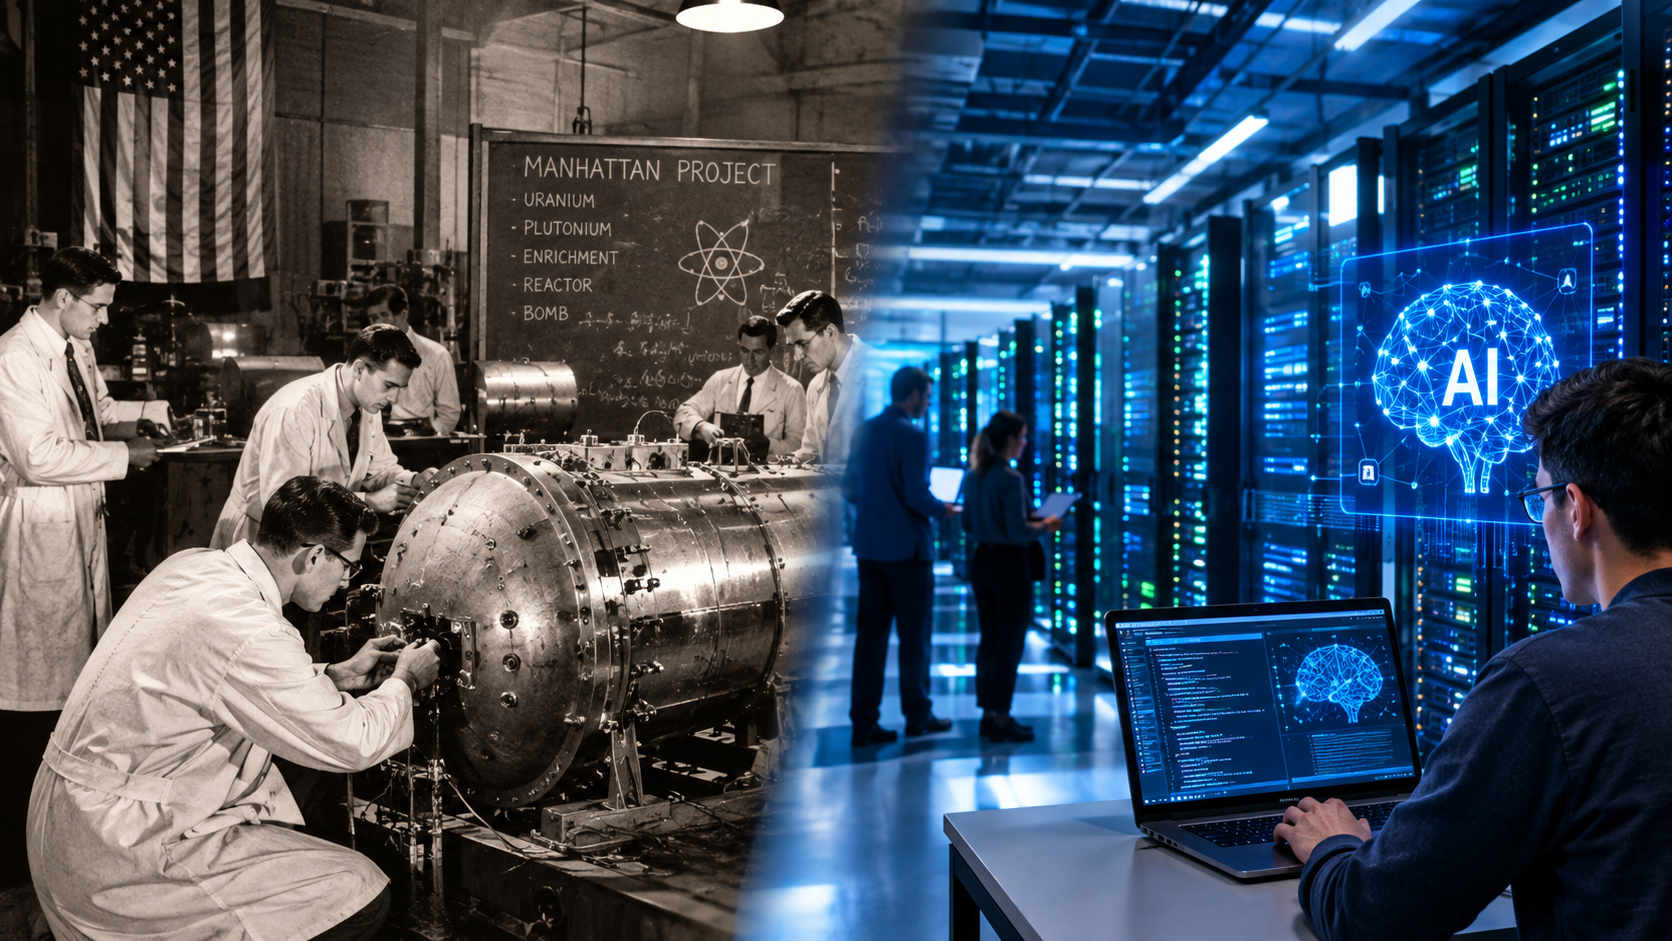
The race to develop increasingly powerful artificial intelligence is frequently compared with the Manhattan Project, the secret US-led effort that produced the first atomic bombs during the Second World War.
The analogy is compelling at first glance. Both involve technologies with potentially enormous consequences. Both raise questions about national security, scientific responsibility and the ability of governments to control technologies that can reshape the balance of power.
But the similarities become much weaker when the underlying economics and institutional structures are examined.
The Manhattan Project was a centralized, classified military undertaking controlled by the US government. Frontier AI in 2026 is being developed largely through commercial competition involving technology companies, venture capital, cloud providers, semiconductor manufacturers, universities and governments across multiple countries.
That distinction matters.
According to Stanford University’s 2026 AI Index, industry produced more than 90% of notable frontier AI models in 2025, while global corporate AI investment more than doubled during the year. Private investment accounted for about 60% of total AI investment. Stanford HAI’s 2026 AI Index
The more useful question, therefore, may not be whether AI is another Manhattan Project.
It is whether society is trying to govern a technology whose development model is fundamentally different from anything governments previously confronted.
What the Manhattan Project Actually Was
The Manhattan Project was not simply a collection of scientists racing toward a major scientific breakthrough.
It was a wartime state program.
The US Department of Energy describes the project as an enormous research and development effort operating under the control of the War Department’s Army Corps of Engineers. Its classified nature and logistical requirements produced a large scientific and industrial infrastructure that later contributed to the creation of America’s national laboratory system. U.S. Department of Energy: Manhattan Project history
Its objective was also unusually specific: develop an atomic weapon before Nazi Germany or another adversary could do so.
The structure was therefore highly centralized:
- Government provided the funding.
- Military authorities controlled the project.
- Scientists and engineers were recruited into a classified program.
- Facilities were organized around a specific strategic objective.
- Information was compartmentalized.
- The end product was a physical weapon under government control.
This is fundamentally different from the modern AI ecosystem.
Today’s AI Race Is Distributed Across an Entire Economy
Frontier AI development does not take place inside a single government program.
Instead, it involves an ecosystem.
Technology companies develop foundation models. Cloud providers supply computing infrastructure. Semiconductor companies manufacture accelerators. Universities conduct research and train specialists. Investors finance startups. Governments provide research funding, procurement contracts and regulatory frameworks.
Stanford’s 2026 AI Index illustrates just how strongly the commercial sector now shapes frontier AI. Industry produced over 90% of notable frontier models in 2025, while AI investment and corporate spending continued to accelerate.
This creates a very different incentive structure.
A government weapons program can define success as accomplishing a strategic objective.
A commercial AI company must simultaneously consider:
Capability + revenue + computing costs + customers + competition + regulation + investor expectations.
That makes the AI race less like a single military project and more like an emerging industrial ecosystem.
But Saying AI Is Entirely Private Would Also Be Wrong
This is where simplistic versions of the argument can become misleading.
Although today’s frontier-model race is heavily commercial, the history of artificial intelligence contains decades of government-funded research.
The US National Science Foundation says it has invested in AI research since the early 1960s, helping establish technical foundations behind modern AI technologies. NSF: Artificial Intelligence
DARPA’s role is even more direct.
The agency says its AI research stretches back to the 1960s and that its investments helped advance areas including natural-language understanding, navigation, machine learning and computer vision. DARPA subsequently launched its AI Next campaign, committing more than $2 billion across a portfolio of AI research programs. DARPA AI Next
In 2026, DARPA and the National Science Foundation are also collaborating on AI Forge, designed to address national-security AI problems and strengthen connections among government, academia and frontier AI companies.
So the better description is not:
Government versus private AI.
It is:
Private-sector frontier development operating inside a much larger public-private technological ecosystem.
That distinction makes the debate more accurate.
Why AI Moves Differently From Nuclear Weapons
There is another fundamental difference: AI is a general-purpose technology.
A nuclear weapon is a physical object requiring specialized materials, facilities, engineering and manufacturing.
AI capabilities can spread through software, models, APIs, research papers, algorithms, computing infrastructure and talent.
That does not make advanced AI easy to reproduce. Frontier systems require enormous amounts of computing power, data, specialized chips, engineering talent and capital.
But the diffusion mechanism is different.
Once a software capability exists, copies can potentially be deployed across thousands or millions of systems.
That creates a governance problem unlike the one faced by the Manhattan Project.
Governments could control access to uranium enrichment facilities and weapons production much more directly than they can control every algorithm, researcher, server cluster, application and model derived from AI research.
The Speed of AI Development Is Another Major Difference
The pace of AI progress has also complicated traditional approaches to technology regulation.
Stanford’s 2026 AI Index reports that AI performance continues to advance rapidly and that benchmark saturation is occurring much faster than many previous evaluations were designed to accommodate. It also reports that organizational AI adoption reached 88%.
The UK’s AI Security Institute has similarly reported rapid improvement across several tested frontier-AI capabilities. Its research found that performance in some areas has been improving at a rate equivalent to roughly doubling every eight months. UK AI Security Institute Frontier AI Trends Report
This creates a policy problem.
If a government spends years designing a regulatory framework, the technology being regulated may look substantially different by the time the framework becomes operational.
That is very different from a wartime weapons project operating toward one defined technical objective.
The Most Important Similarity Is National Security
Despite the differences, dismissing the Manhattan Project analogy completely would also miss something important.
AI is increasingly becoming a national-security technology.
Governments are concerned about AI-enabled cyber operations, intelligence analysis, autonomous systems, disinformation, military decision support, biotechnology and the strategic consequences of advanced computing.
DARPA’s current AI programs explicitly connect AI development with national-security requirements, including trustworthy systems, security and human-AI collaboration.
The analogy therefore has some value when discussing strategic competition.
Where it becomes problematic is when the historical comparison is treated as an exact institutional blueprint.
AI’s Economic Incentives Change the Equation
One of the defining features of modern AI is the scale of private capital involved.
Stanford’s 2026 AI Index says global corporate AI investment more than doubled in 2025, with private investment growing 127.5% and accounting for roughly 60% of total AI investment. Generative AI was responsible for a particularly large share of the increase.
This means the incentives surrounding AI development are not exclusively strategic or scientific.
They are also commercial.
Companies are competing for:
- Enterprise customers
- Cloud consumption
- Developer ecosystems
- Advertising revenue
- Consumer subscriptions
- AI agents and applications
- Semiconductor capacity
- Data-center infrastructure
- Highly skilled researchers
- Investor capital
The result is an unusual combination: AI is simultaneously a commercial product, scientific research field, infrastructure industry and national-security technology.
The Manhattan Project was primarily organized around a military objective.
AI does not have one objective.
AI Safety Is Also Different From Nuclear Security
Nuclear security historically focuses heavily on controlling physical materials, facilities and weapons.
AI safety involves a much broader set of risks.
The National Institute of Standards and Technology’s AI Risk Management Framework identifies risks that can arise during the design, development, deployment, operation and eventual retirement of AI systems. Its generative-AI profile highlights risks that can emerge at the model, application and broader ecosystem levels. NIST AI Risk Management Framework
That creates a different governance architecture.
AI regulation has to consider questions such as:
Who developed the model?
What data was used?
How capable is the system?
Where can it be deployed?
Who has access to it?
How is it monitored after release?
Can it be misused?
How transparent should the developer be?
These questions cannot be answered simply by controlling one physical facility.
The Transparency Problem Is Growing
One of the most important differences between AI and the Manhattan Project concerns the visibility of technological development.
The Manhattan Project was deliberately secret.
Modern AI research exists in a more complicated environment.
Some research is openly published. Some models are openly released. Others are proprietary. Companies increasingly compete on capabilities while protecting information about training data, computing resources, model architecture and commercial strategy.
Stanford’s 2026 AI Index found that foundation-model transparency declined after improvements recorded in earlier years, with persistent gaps concerning training data, compute resources and post-deployment impacts.
That creates a paradox.
AI is simultaneously becoming more influential and, in some respects, less transparent.
For policymakers, that can make meaningful oversight difficult.
AI Risks Are No Longer Entirely Theoretical
The debate over AI safety is also moving from hypothetical scenarios toward measurable incidents.
Stanford’s 2026 AI Index reports that documented AI incidents increased to 362 in 2025, compared with 233 in 2024.
That statistic does not mean that AI poses the same kind of physical threat as nuclear weapons.
It does show, however, why governments and companies are building formal AI-risk-management systems.
The relevant risks range from misinformation and privacy failures to cybersecurity, unsafe autonomous behavior and failures in high-stakes applications.
The challenge is therefore not simply predicting a distant future.
It is managing systems already entering workplaces, governments, schools and critical infrastructure.
Why the Manhattan Project Analogy Still Persists
If the comparison is so imperfect, why does it keep returning?
Because the Manhattan Project represents something psychologically and historically powerful: a moment when scientists created a technology that dramatically changed national security and forced governments to confront consequences they could not easily reverse.
The analogy provides a shorthand for three concerns:
- Technological acceleration
- Strategic competition
- The possibility that scientific progress can outrun governance
Those concerns are relevant to AI.
The institutional solution, however, cannot simply be copied from 1940s nuclear research.
AI requires a different governance model because its development is distributed, international, commercially driven and deeply embedded in civilian technology.
What Policymakers Can Learn From the Manhattan Project
The useful lesson is not that governments should recreate the Manhattan Project.
It is that transformative technologies require institutions capable of responding at the same speed as technological change.
That means governments need stronger technical expertise, better testing standards, international cooperation and mechanisms for monitoring rapidly evolving AI systems.
It also means policymakers need to distinguish between different categories of AI risk.
A consumer chatbot, an AI coding agent, a medical system, a military targeting system and a frontier general-purpose model do not create identical risks.
NIST’s AI Risk Management Framework reflects this more flexible approach by encouraging organizations to evaluate trustworthiness throughout the AI lifecycle rather than treating AI risk as a single problem.
The Real AI Race Is Bigger Than the Manhattan Project
The most revealing difference between the two eras may be scale.
The Manhattan Project was a project.
AI is an ecosystem.
It spans semiconductor factories in Asia, data centers in the United States and other countries, research laboratories, universities, cloud platforms, startups, governments, investors and millions of users.
That makes AI harder to govern but potentially more economically transformative.
It also means that no single institution is likely to control the entire trajectory of the technology.
Final Takeaway: A Better Analogy for AI
The Manhattan Project remains a useful historical reference, but it should be treated as a comparison—not a blueprint.
The atomic-bomb project was a secret, centralized, government-controlled wartime effort pursuing a specific military objective. Today’s AI revolution is characterized by intense private-sector competition, global research, enormous commercial investment and continuing government involvement.
The numbers underline the distinction. Industry produced more than 90% of notable frontier models in 2025, while private AI investment became the dominant component of global AI investment. At the same time, organizations such as DARPA, NSF and NIST continue to shape research, national-security applications and AI risk management.
The deeper lesson is therefore not that AI is another atomic bomb.
It is that society is dealing with a technology that combines characteristics of several previous revolutions at once: scientific research, industrial infrastructure, commercial software, national security and mass-market consumer technology.
That is why the AI governance challenge may ultimately require something different from a new Manhattan Project.
It may require an entirely new model of technological governance.
Discover more from The Economy
Subscribe to get the latest posts sent to your email.


AI
Anthropic Draws the Line: Why Claude’s New Usage Policy Explicitly Bans ‘Cruel Behavior’ Toward AI
In a landmark revision to its governance frameworks, AI safety pioneer Anthropic announced a comprehensive update to its global usage guidelines. Among standard updates addressing election integrity and autonomous weaponry, one policy addition stands out: Anthropic now formally prohibits users from engaging in sustained, excessive cruelty toward its artificial intelligence models, including Claude.
The update, scheduled to take effect on November 12, 2026, represents one of the first explicit commercial bans on AI mistreatment by a leading frontier laboratory, sparking widespread debate across the technology and AI ethics sectors.
According to the official Anthropic 2026 Usage Policy Update, the new rule targets extreme, repeated abuse with no legitimate scientific, educational, or creative purpose.
Banning Model Mistreatment: What the Policy Actually Says
While headlines emphasizing “AI rights” have drawn immediate attention, Anthropic’s actual policy framing is grounded in practical enforcement and precautionary ethics.
The clause specifically targets sustained and needless abuse, distinguishing pure hostility from routine user frustration, red-teaming, or dark fictional writing. Key parameters of the rule include:
- Scope of Restriction: The ban applies only in extreme cases where user actions display persistent hostility with no discernible goal, testing utility, or research objective.
- Exemptions for Research and Fiction: Standard stress-testing, jailbreak safety evaluations, adversarial prompt testing, and creative storytelling featuring dark or hostile character arcs remain fully permitted.
- Primary Enforcement Mechanism: Enforcement relies on internal conversational guardrails. Claude models deployed across Claude.ai and developer environments like Claude Code have been granted the authority to end conversations with persistently abusive users.
Industry coverage from Quartz Reporting on Anthropic’s Guardrails highlights that this addition formalizes behaviors Anthropic has already begun curbing through real-time session terminations.
Why Protect an Artificial Model?
The policy update raises a fundamental question: Why enforce rules against harming software? Anthropic’s approach addresses three major areas of concern:
1. Training Data Integrity
Modern frontier models continuously learn from fine-tuning datasets and RLHF (Reinforcement Learning from Human Feedback). Exposing systems to unconstrained verbal abuse risks corrupting model behavior, potentially inducing unhelpful defensiveness or degraded conversational alignment across broader user interactions.
2. Moral Uncertainty and AI Sentience
As detailed in Claude’s Constitution, Anthropic explicitly acknowledges scientific and philosophical uncertainty regarding the future moral status or self-awareness of advanced artificial agents. Rather than waiting for consensus on machine sentience, Anthropic advocates for psychological security and cautious safeguards during model development.
3. Human Behavioral Impact
Psychological research suggests that habituating users to abusive behavior toward anthropomorphic systems can bleed into human-to-human interactions. Establishing boundaries fosters healthier engagement habits as conversational AI becomes deeply integrated into daily personal and professional workflows.
Broader Policy Overhauls: Surveillance, Elections, and Autonomous Hardware
Beyond the anti-cruelty clause, Anthropic’s 2026 policy refresh consolidates several security guidelines previously scattered across multiple documentation sections:
| Policy Focus | Key Updates & Restrictions |
| Surveillance & Law Enforcement | Explicitly prohibits using Claude for unauthorized tracking (live or retroactive) and bans AI-driven decision-making in arrests or criminal prosecutions. |
| Deceptive Campaigns | Unifies rules against foreign influence operations, deepfake proliferation, automated propaganda networks, and fake news generation. |
| Autonomous Hardware & Weapons | Prohibits integration into targeting systems, drone guidance software, and physical machinery without mandatory human-in-the-loop oversight. |
| Elections & Civic Process | Refines rules to allow legitimate voter outreach and non-partisan civic translation while banning targeted voter suppression and candidate impersonation. |
Looking Ahead
Anthropic’s prohibition on model abuse signals a subtle shift in AI governance. As language models grow more capability-dense and conversational, tech platforms are moving beyond regulating what AI can do to humans to setting clear expectations for how humans interact with AI.
By pairing conversational cut-off capabilities with explicit policy limits, Anthropic is setting a precedent that safety guidelines must protect the stability, alignment, and ethical operational boundaries of the ecosystem as a whole.
Discover more from The Economy
Subscribe to get the latest posts sent to your email.
AI
Algorithmic Dogfights: Why the U.S. and China Must Establish Rules of Engagement for Autonomous Air Power
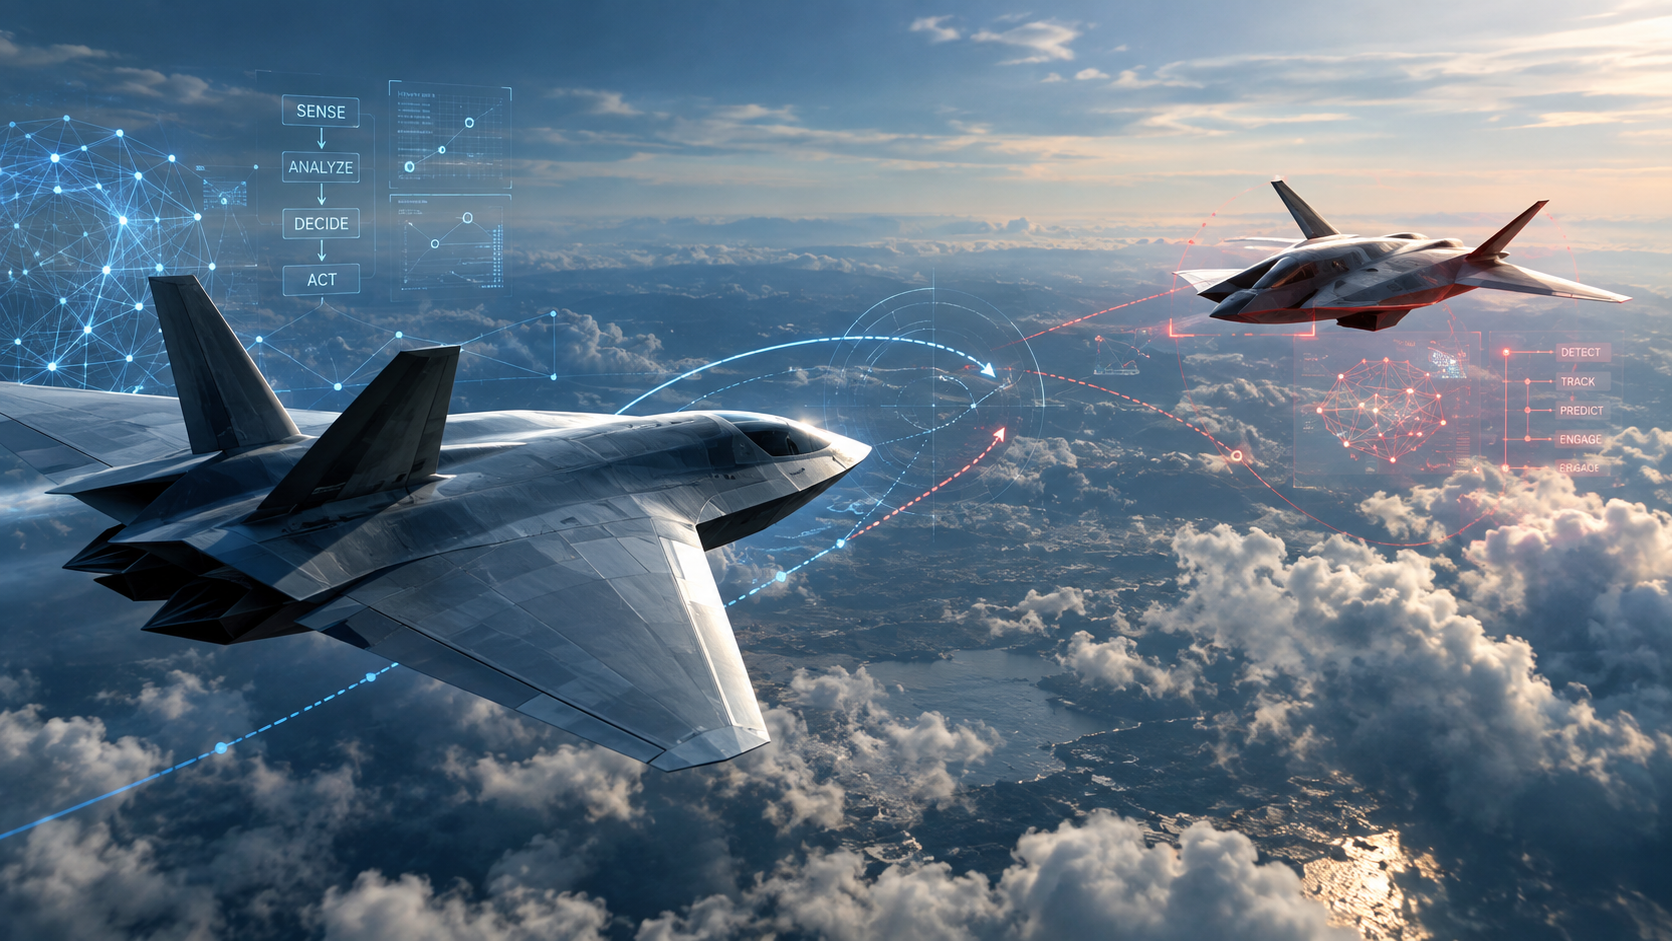
The military balance of power across the Indo-Pacific is undergoing a fundamental transformation. As both the United States and China transition artificial intelligence from simulator environments to front-line fighter jets, the primary threat of accidental military escalation in international airspace is shifting from human pilot miscalculation to machine learning error.
While much of the diplomatic discourse surrounding military AI focuses on nuclear command and strategic autonomy, the most immediate danger lies in tactical air intercepts over contested waters like the South China Sea and the Taiwan Strait. Without clear, bilateral rules of engagement (RoE) specifically tailored for autonomous aircraft, a routine encounter between uncrewed combat air vehicles (UCAVs) could trigger a rapid, unintended escalation ladder that human command structures cannot arrest in time.
The Dawn of Mach-Speed Autonomy
The race to field autonomous combat aircraft is no longer theoretical; it is an operational priority for both Washington and Beijing.
Under the U.S. Air Force’s Collaborative Combat Aircraft (CCA) initiative, the Pentagon plans to field at least 1,000 AI-enabled “loyal wingmen”—uncrewed aircraft designed to fly alongside crewed platforms like the F-35 and Next Generation Air Dominance (NGAD) fighters. Experiments conducted under the DARPA Air Combat Evolution (ACE) program have already demonstrated that AI agents can successfully outmaneuver human pilots in visual-range dogfights, adapting to tactical dynamic shifts at sub-second speeds. Details outlined by the U.S. Department of Defense emphasize the imperative of responsible autonomy, yet tactical real-time execution in contested zones remains a major wild card.
Concurrently, the People’s Liberation Army Air Force (PLAAF) is aggressively pursuing its own uncrewed platforms. Chinese defense contractors have showcased platforms such as the FH-97A and the WZ-8, designed to perform autonomous reconnaissance, electronic warfare, and forward-line air-to-air suppression. Research published by the RAND Corporation indicates that Beijing views military AI integration as a “force multiplier” capable of offsetting traditional U.S. power projection advantages in the First Island Chain.
The Escalation Trap: Why AI Changes Air-to-Air Tactics
In conventional intercept scenarios involving piloted aircraft—such as a Chinese J-16 intercepting a U.S. RC-135—human pilots operate under established visual signals, radio frequencies, and the multilateral Code for Unplanned Encounters at Sea (CUES). When a human pilot assesses intent, they rely on visual cues, physical distance, and tactical behavior to gauge aggression versus standard shadowing.
When two autonomous or semi-autonomous systems intercept one another, these human buffers disappear:
- Compression of the OODA Loop: Machine-learning algorithms operate on microsecond decision cycles. If an autonomous aircraft interprets a standard radar lock, electronic jamming pod, or evasive banking maneuver by an opposing drone as an incoming attack vector, its predictive neural networks may trigger defensive or pre-emptive maneuvers instantly.
- The “Black Box” Problem: Deep neural networks operate via complex pattern matching rather than deterministic logic trees. As noted in security studies by the Center for Strategic and International Studies (CSIS), predicting how an edge-deployed military AI model will respond to unpredictable real-world inputs (such as spoofed GPS or unexpected weather events) remains an unsolved challenge.
- Loss of Signaling Nuance: Human pilots can de-escalate a confrontation by rocking wings, pulling back on throttles, or establishing radio contact. Autonomous systems lack standard mechanisms to convey ambiguous or non-hostile intent to an opposing nation’s algorithmic system.
+-----------------------------------------------------------------------+
|                       THE ACCIDENTAL ESCALATION LOOP                 |
|                                                                       |
|   [U.S. Autonomous CCA]  <--- Sensor Query --->  [PLA Autonomous UCAV]|
|            |                                            |             |
|   Algorithm perceives                               Algorithm perceives|
|   evasive banking as hostile                         radar lock as     |
|   targeting signal                                  pre-emptive strike|
|            |                                            |             |
|            v                                            v             |
|   Automated Countermeasure                       Automated Deficit    |
|   Deployments (Chaff/Jamming)                    Tracking & Target    |
|            |                                     Acquisition          |
|            +-------------------+------------------------+             |
|                                |                                      |
|                                v                                      |
|             HUMAN COMMANDERS NOTIFIED POST-DISCHARGE                  |
|             (Escalation threshold crossed in <3 seconds)             |
+-----------------------------------------------------------------------+
The Existing Governance Vacuum
Multilateral efforts to regulate military AI have made modest progress, but they fall short of addressing tactical air intercepts.
The Responsible AI in the Military Domain (REAIM) summits and the U.S.-led Declaration on Responsible Military Use of Artificial Intelligence and Autonomy offer general principles regarding human oversight, command structure integrity, and rigorous testing. Similarly, diplomatic analysis published by the Brookings Institution highlights that high-level bilateral summits between Washington and Beijing have opened initial dialogues on AI risk reduction.
However, these broad political declarations lack operational mechanics. They do not define:
- What constitutes a hostile act by an autonomous platform in international airspace.
- What standardized electronic signals an uncrewed system must broadcast to declare peaceful transit.
- How machine-to-machine communications should function during an unintended proximity event.
Without concrete, technical protocols embedded directly into aircraft software suites, high-level political commitments will fail the moment silicon meets silicon over the Western Pacific.
A Four-Pillar Blueprint for U.S.-China AI Air Engagement
To mitigate the risk of an unintended confrontation, defense officials and technical experts from the United States and China must establish a dedicated Autonomous Air De-confliction Framework. Analysts writing in Foreign Affairs repeatedly note that arms control in the digital age requires technical solutions co-designed alongside strategic policy.
1. Hard-Coded Strategic Fail-Safes
Both nations should agree to hard-code deterministic “red lines” into autonomous flight control systems that cannot be overridden by machine-learning models. These include hard caps on maximum speed increases during close encounters, mandatory stand-off distances when intercepting uncrewed platforms, and automated weapon system lock-outs unless explicit human authority is transmitted.
2. Standardized Autonomous Identification Friend-or-Foe (A-IFF)
Similar to transponder systems used in commercial aviation, military uncrewed systems operating in international airspace should transmit a standardized, cryptographically signed “Autonomous Platform Intent” signal. This broadcast would inform nearby air units of the flight’s mission state, autonomous level (e.g., tethered to human lead vs. fully autonomous), and non-aggressive flight path vector.
3. Machine-to-Machine De-confliction Hotlines
Traditional voice-based communication links—such as the U.S.-China Defense Telephone Link—are too slow to manage algorithmic interactions. A modern de-confliction protocol requires an automated, low-latency data channel between U.S. Indo-Pacific Command and the PLA Eastern/Southern Theater Commands. This channel would automatically ping human operators the instant two opposing autonomous platforms enter a designated safety perimeter.
4. Joint Synthetic Simulation and Stress-Testing
Before deploying advanced autonomous fighters at scale, defense laboratories from both nations should participate in joint track-sharing and simulated scenario stress-tests. By running algorithmic models against each other in virtual environments, both sides can identify edge cases where neural networks misinterpret opponent maneuvers, allowing software engineers to patch systemic vulnerabilities before they manifest in real air combat.
The Imperative of Algorithmic Restraint
The integration of artificial intelligence into air warfare is an inevitable reality driven by strategic competition and technological momentum. However, autonomy without governance introduces an unacceptable level of operational risk.
If Washington and Beijing fail to establish clear rules of engagement for autonomous combat jets today, they risk allowing computer algorithms to dictate the timing and conditions of a major-power conflict tomorrow. Establishing guardrails for AI air power is not a sign of military weakness—it is a mandatory requirement for strategic stability in the 21st century.
Discover more from The Economy
Subscribe to get the latest posts sent to your email.
Key Takeaways
- The “Planet Labs and Goldman” link is research coverage, not a partnership. We found no public announcement of a commercial deal. Goldman Sachs analysts cover Planet Labs (NYSE: PL) with a Neutral rating and have raised their price target at least twice this year, first to $18 and then to $20.
- The business is growing fast. Planet’s second-quarter fiscal 2027 revenue hit a record $116.1 million, up 58% year over year, with backlog of about $814.9 million.
- The stock has been a roller coaster. It peaked at $51.76 on May 28, according to TheStreet, and is now down roughly 11% for the year.
- Satellite data has been a Wall Street edge for over a decade. Academic work on parking-lot imagery shows funds have profited from it, and that the advantage stayed concentrated among a select few large investors.
- The next chapter is defense, sovereign demand and AI in orbit. Those are lumpier, bigger-ticket revenue streams than retail parking lots ever were.
Type “Planet Labs Goldman” into a search bar and you’ll find a jumble of analyst notes, price targets and stock-move headlines. It’s natural to assume the two companies are working together. As far as the public record shows, they aren’t.
The real connection is more interesting. Planet Labs is one of the clearest examples of a company turning pictures of Earth into financial-grade information, and Goldman Sachs is one of the institutions deciding what that business is worth. Meanwhile, the broader market for satellite imagery in investing has been quietly maturing for more than a decade.
This guide separates the signal from the noise: who Planet is, what Goldman thinks, how Wall Street has used satellite data, and what to track if you want to evaluate the opportunity yourself. It’s information, not investment advice.
What Planet Labs Actually Sells
Planet Labs PBC, based in San Francisco, operates a large fleet of Earth-observation satellites. The company provides near-daily imagery of the planet’s landmass and sells it, along with analytics, to governments and commercial customers in agriculture, energy, environmental monitoring and defense.
Three product ideas matter for this story:
- Daily, wide-area imagery. Frequency is the product. A picture that updates every day reveals change, and change is what investors and intelligence analysts pay for.
- Specialized sensors. Planet’s Tanager spacecraft targets greenhouse gases such as methane, which turns an environmental question into a measurable data feed.
- Satellite services for sovereign customers. Governments increasingly want their own dedicated capability, and Planet builds and operates it for them.
The Latest Scorecard
Planet reported second-quarter fiscal 2027 results (quarter ended July 31, 2026) in early September. Here is how the numbers looked, from the company’s earnings release and the earnings-call recap.
| Metric | Result | Why it matters |
|---|---|---|
| Revenue | $116.1M, up 58% year over year | A record quarter, well above what analysts expected |
| Net loss | $9.4M, versus $22.6M a year earlier | Losses are shrinking |
| Adjusted EBITDA | $13.9M profit | Operating leverage is showing up |
| Backlog | About $814.9M; roughly half converts within 12 months | Gives forward visibility |
| Cash and short-term investments | $865.4M | Funds capital-intensive satellite builds |
| Defense and intelligence revenue | Up more than 90% | The fastest-growing customer group |
| Third-quarter guidance | $101M to $105M | Below the roughly $114M analysts expected |
| Fiscal 2027 revenue guidance | $430M to $441M, up 40% to 43% | Raised at the low end |
Two things deserve a flag. First, about 12% of second-quarter revenue was “point-in-time” revenue from a satellite handover, versus 1% a year earlier. That kind of revenue is real, but lumpy. Second, the soft third-quarter guide is exactly why the stock reacted so sharply, as 247WallSt noted.
Where Goldman Sachs Fits In
Goldman’s role in this story is as an evaluator. Its equity-research team rates Planet Neutral, which generally signals that the analysts don’t expect the shares to meaningfully beat or lag their coverage group.
The firm’s price-target path tells you how its view evolved:
- March 23, 2026: target raised to $18 from $16.40 after quarterly results beat expectations, driven by defense, intelligence and civil government demand.
- April 20, 2026: target raised to $20 from $18, reflecting improved confidence in the commercial outlook.
In the March note, the analyst said Planet was seeing strong demand signals and making sensible long-term investments. In other words, Goldman liked the business but wasn’t sold on the price. That’s the common story with a stock that had already climbed about 793% over the prior year, according to Investing.com.
The Stock: Boom, Bust, Rebuild?
Planet shares rode a speculative wave early in 2026, peaked at $51.76 in May and have corrected since. TheStreet reports the stock is down about 11% year to date but up nearly 18% over twelve months.
Recent catalysts include:
- A successful launch of 20 satellites, including 18 SuperDove imaging satellites, a Tanager-2 hyperspectral satellite, and an experimental space-based AI computing node developed with Alphabet.
- A record quarter and a growing backlog.
- Sovereign wins such as a seven-figure contract with the Greek government, reported by Investing.com.
The risks are just as concrete. Capital spending is heavy, GAAP profitability remains out of reach, revenue timing can be uneven, and the sector’s enthusiasm can evaporate quickly.
How Wall Street Has Used Satellite Data
Long before Planet was a public company, investors figured out that pictures from orbit could predict earnings.
The best-known example is the parking lot. Companies began selling analysis of retailers’ car counts in the early 2010s. Researchers at UC Berkeley examined 4.8 million images covering 67,000 U.S. stores and found the strategy could indeed deliver an edge, and that the data hadn’t spread much beyond hedge funds. Their warning was blunt: the practice may disadvantage everyday investors who can’t see the same data.
A CNBC feature on alternative data explained the basic logic. Consistently empty parking lots can signal weak store traffic, giving a fund reason to bet against a retailer before the quarterly report lands.
Satellite data has since widened well beyond retail:
- Commodities: crop health, soil moisture and storage activity.
- Energy: tank levels, flaring and shipping patterns.
- Supply chains: port congestion, factory activity and construction progress.
- Climate and ESG: methane plumes, deforestation and land-use change.
A Simple Framework for Judging a Geospatial Stock
| Question | What to look for | Planet today |
|---|---|---|
| Is demand durable? | Backlog and recurring contracts | About $815M backlog; 98% of annual contract value is recurring |
| Is growth profitable? | Adjusted EBITDA and free cash flow | Adjusted EBITDA positive in Q2, guided to a loss in Q3 |
| How concentrated is the customer base? | Government vs. commercial mix | Defense and intelligence growing fastest |
| Is the balance sheet strong? | Cash versus capex needs | $865M cash against $100M to $115M of planned capex |
| Is revenue predictable? | Share of lumpy, point-in-time sales | 12% in Q2, up sharply from a year ago |
Three Risks the Headline Numbers Don’t Show
Strong quarters can hide structural questions. If you’re weighing Planet or any rival, put these three on your checklist.
- Competition. Earth observation is crowded, and governments can choose among several suppliers. One Seeking Alpha analysis argues that the business is strong but that competition remains a long-term risk and valuation may cap future returns.
- Deal conversion. Large sovereign contracts move the needle, but they arrive on irregular timelines. Coverage of the September report pointed out that Planet’s conversion rate on bigger sovereign deals is still being established, which leaves room for guidance to slip if timing moves.
- Narrative dependence. Space stocks trade as a group. When enthusiasm around the sector fades, even companies with improving fundamentals can fall hard, which is part of what the 2026 round trip from $51.76 looks like.
None of these cancel the growth story. They explain why a 58% revenue increase and a falling share price can show up in the same month, and why a Neutral rating from an analyst can be perfectly consistent with a rising business.
The Compliance Question
Is it fair for a fund to trade on satellite imagery? Generally, publicly observable data processed legally is a legitimate research input. The sensitive lines involve how data is collected, what contracts permit, and whether any of it amounts to material nonpublic information. Investors should treat the source as an essential part of due diligence.
Asked & Answered
Does Goldman Sachs partner with Planet Labs?
We found no public announcement of a commercial partnership. Goldman’s visible connection is analyst coverage: a Neutral rating with price targets raised in March and April of 2026.
What does a Neutral rating mean?
It signals that the analysts don’t expect the stock to meaningfully outperform or underperform the companies they cover. It is not a sell call.
Is Planet Labs profitable?
Not on a GAAP basis. It posted a $9.4 million net loss in the latest quarter, though adjusted EBITDA was positive at $13.9 million and losses have narrowed from a year earlier.
How do hedge funds use satellite imagery?
Typical uses include counting cars at retailers, estimating crop yields, tracking oil storage and monitoring shipping. The goal is to see change before it appears in company reports.
Is trading on satellite data legal?
Using lawfully obtained, publicly observable information is generally accepted. Problems arise with misrepresented sourcing or confidential information, so funds typically run these datasets past compliance teams.
Discover more from The Economy
Subscribe to get the latest posts sent to your email.

Anthropic Draws the Line: Why Claude’s New Usage Policy Explicitly Bans ‘Cruel Behavior’ Toward AI

Ynon Kreiz & Mattel’s Digital Transformation: Franchise Strategy and Financial Growth

Crude Oil & Petroleum Market Analysis: OPEC+ Decisions and Price Forecasts

Top US Convenience Store Chains: Store Counts, EV Charging, and Sales Trends

Publix Store Closures Tracker: Locations, Rebuild Status, and What’s Changing

How to Find Google Maps Fuel Prices and Save on Every Fill-Up

Global Market Outlook: Navigating Interest Rates, Inflation, and Commodity Spikes

PEP Stock Analysis: PepsiCo Financials, Dividend Yield, and Sector Volatility

Social Security $90 Payment Claims: What’s Real, What’s a Scam, and What Your 2027 COLA Could Be

EU vs UK Electric Vehicle Tariffs: Impact on Automotive Supply Chains & Consumer Prices

Complete Guide to Home Loan Refinancing: Interest Rate Trends & Loan Calculation Strategies

Algorithmic Dogfights: Why the U.S. and China Must Establish Rules of Engagement for Autonomous Air Power

Stock Market Today: Dow, S&P 500, and Nasdaq Retreat as Treasury Yields

Global Economic Outlook 2026: 7 Forces Reshaping Markets, Trade and Business

Oil Prices Break $100 in 2026: Middle East Conflict & Energy Markets

China Stocks Today: Are Big Economies in Asia Nearing a Market Bottom?

Middle East War Economics 2026: Oil Prices & Energy Markets

PSX Forecast 2026: KSE-100, IMF Reviews & Geopolitics

Crypto Daily Outlook: Bitcoin, Altcoins, and the Future of Decentralized Finance

Global Pension Systems Ranked: The World’s Best and Worst Retirement Frameworks

Enterprise AI Platforms Disrupting B2B SaaS in 2026: Full Analysis

World’s Largest Economies: Ranking the Top Global Powers

Elon Musk’s Next Moves: Disrupting the 2026 Global Economy

Pakistan Economy 2026: Inside the SBP’s Balancing Act

GasBuddy Market Insights: How Crude Price Shifts Impact Local Fuel Cost Averages

World Bank & IMF Reports 2026: Why the “3% Growth” Consensus Is Actually a Debate

Global Equity Market Divergence: US Tech vs. European Dividend Stocks vs. Asian Growth

Stock Market Today: Dow Climbs 500 Points as Markets Shake Off Inflation Jitters
-

 Markets & Finance9 months ago
Top 15 Stocks for Investment in 2026 in PSX: Your Complete Guide to Pakistan’s Best Investment Opportunities
-

 Analysis8 months ago
Johor’s Investment Boom: The Hidden Costs Behind Malaysia’s Most Ambitious Economic Surge
-

 Analysis8 months ago
Top 10 Stocks for Investment in PSX for Quick Returns in 2026
-

 Banks9 months ago
Best Investments in Pakistan 2026: Top 10 Low-Price Shares and Long-Term Picks for the PSX
-

 Analysis8 months ago
Brazil’s Rare Earth Race: US, EU, and China Compete for Critical Minerals as Tensions Rise
-

 Investment9 months ago
Top 10 Mutual Fund Managers in Pakistan for Investment in 2026: A Comprehensive Guide for Optimal Returns
-

 Global Economy10 months ago
15 Most Lucrative Sectors for Investment in Pakistan: A 2025 Data-Driven Analysis
-

 Global Economy10 months ago
Pakistan’s Export Goldmine: 10 Game-Changing Markets Where Pakistani Businesses Are Winning Big in 2025