
Cybersecurity
Singapore Banking’s Real Test: Beyond Profits, Who Will Safeguard Financial Trust?

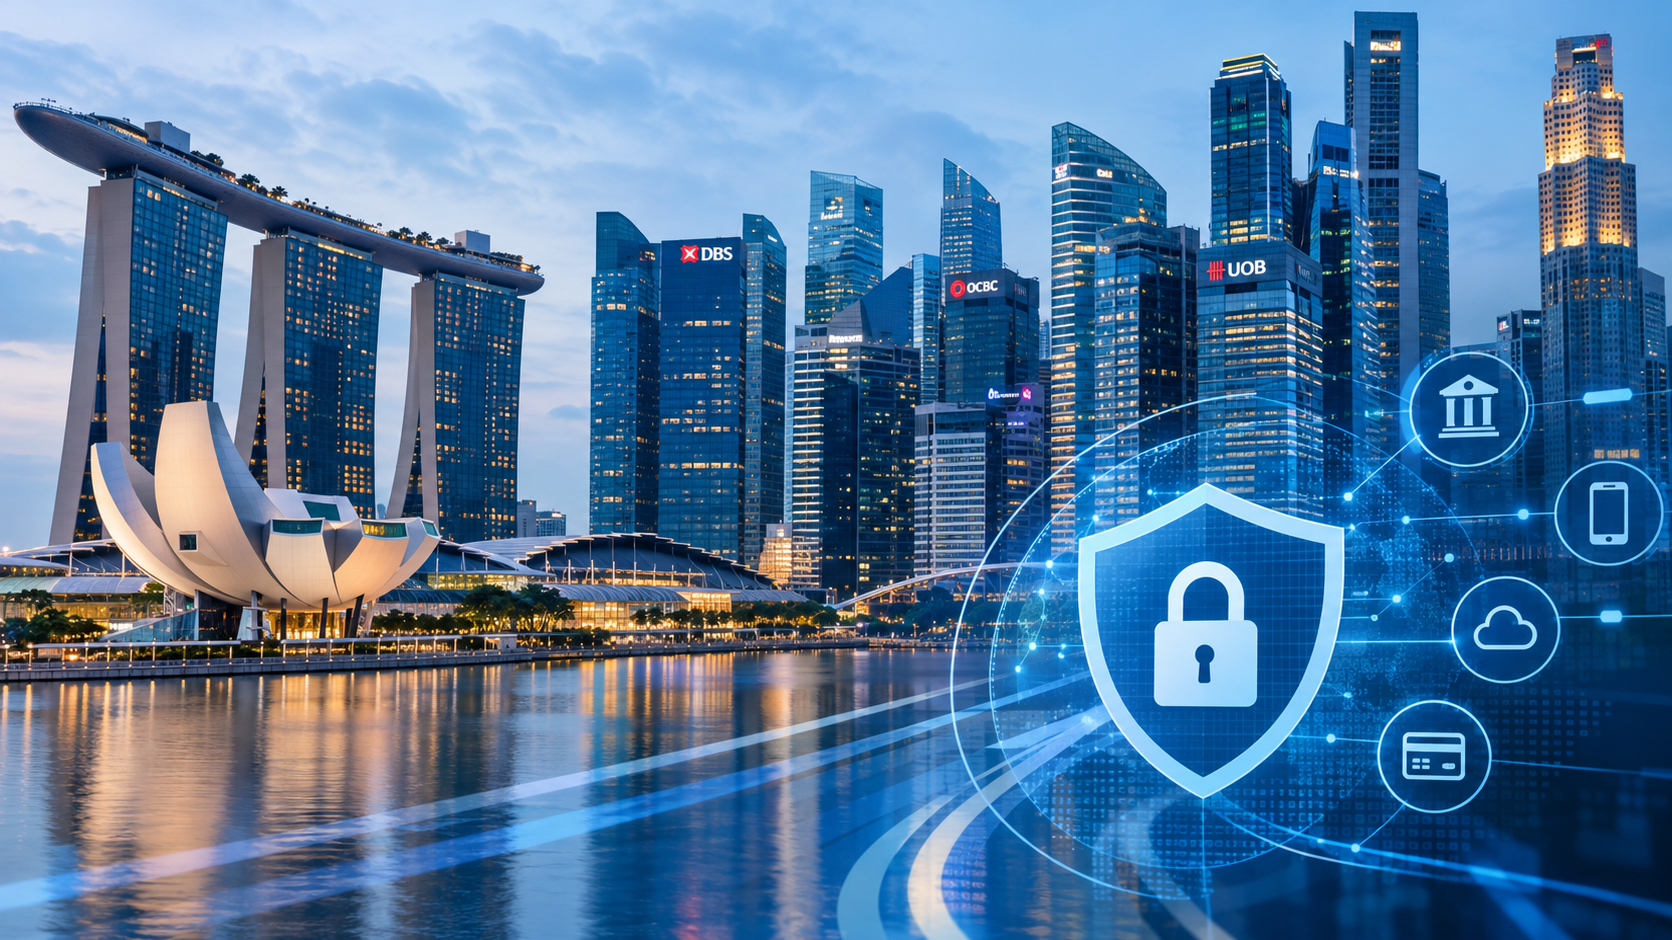
As shares in DBS, OCBC and UOB come under pressure despite resilient underlying businesses, Singapore must ask a question that goes beyond how much its banks can earn: Can its financial institutions continue to honour the public’s trust amid mounting pressures from costs, technological transformation and financial security?
A bank can possess substantial capital, stable deposits and impressive profits, yet still lose the patience of some investors. That is precisely the situation unfolding in Singapore’s financial markets in the autumn of 2026.
Shares in DBS Group, Oversea-Chinese Banking Corporation (OCBC) and United Overseas Bank (UOB) faced sustained pressure from October into early November. Market discussions shifted from dividend returns towards net interest margins, trading income and valuation risks.
Yet the underlying businesses remained remarkably resilient.
According to data compiled by the Singapore Exchange on November 6, the three major banks generated a combined S$8.302 billion in net interest income during the third quarter, marking the 16th consecutive quarter in which their combined net interest income exceeded S$8 billion.
These figures are not contradictory.
A financially sound bank is not necessarily a stock whose price must continually rise. Equally, a declining share valuation does not automatically indicate a systemic threat to deposit safety.
But if the discussion remains confined to how far bank shares have fallen and whether investors should buy them, Singapore risks overlooking a far more consequential public-policy question:
How can its banking industry restore the balance between profitability, customer protection, technological innovation and financial inclusion?
A November 6 report by Lianhe Zaobao highlighted the divergence in the three banks’ third-quarter performances. OCBC exceeded market expectations, while DBS and UOB fell short of some forecasts.
The important task is not to identify a single explanation for every movement in their share prices. It is to distinguish sustainable earnings from exceptional returns, determine which sources of income can be replicated, and understand who ultimately bears the costs of an increasingly complex financial system.
The First Test: Bank Profits Are More Than a Single Number
Net profit is the figure investors notice most readily. Yet its underlying composition often receives considerably less attention.
Interest income, wealth-management fees, insurance earnings, investment gains and trading revenue all contribute to a bank’s financial statements. Their predictability and resilience, however, differ substantially.
Interest earned from long-term lending depends on funding costs and customer demand. Trading income may change rapidly with market conditions. Insurance earnings can be influenced by investment valuations and other exceptional factors.
According to the Singapore Exchange’s third-quarter summary, the three banks recorded approximately 2 per cent quarter-on-quarter growth in net interest income, while non-interest income declined 18.5 per cent.
Looking only at the first figure might suggest that banks continue to perform strongly. Looking exclusively at the second could create the impression that their businesses have suddenly deteriorated.
Neither interpretation is sufficient.
A sound assessment must consider the revenue mix, one-off items and the durability of long-term customer relationships.
DBS reported third-quarter net profit of S$2.81 billion, a 5 per cent decline from a year earlier. At the same time, its wealth-management assets rose to S$544 billion, while its non-performing loan ratio improved to 0.9 per cent.
OCBC reported third-quarter net profit of S$2.04 billion, an increase of 3 per cent year on year. Its net profit for the first nine months of 2026 reached S$6.24 billion.
Meanwhile, UOB’s financial disclosures showed third-quarter net profit of S$1.25 billion, a net interest margin of 1.68 per cent and a non-performing loan ratio of 1.5 per cent.
These figures support two conclusions that can coexist.
Singapore’s banks retain substantial operational strengths. But investors also have legitimate reasons to reassess the pace of future earnings growth.
Treating an exceptionally profitable quarter as a permanent benchmark can inflate the expectations embedded in share prices. Conversely, dismissing a bank’s long-term value because trading income weakened in a single quarter reflects an equally short-term perspective.
The Second Test: Higher Interest Rates Do Not Necessarily Mean Higher Bank Profits
The proposition that higher interest rates automatically produce greater bank profits is one of the financial market’s most persistent oversimplifications.
Banks can certainly earn more from loans and other interest-bearing assets when rates rise. But they must also pay interest to depositors while managing funding maturities, competition, hedging arrangements and borrowers’ repayment capacity.
When deposit costs increase faster than lending yields, net interest margins can narrow rather than widen.
An October analysis by The Business Times had already drawn attention to this changing reality. Earlier market optimism about rising rates may have underestimated the pressure of funding costs.
Bank management cannot rely exclusively on the broader interest-rate environment to establish a sustainable competitive advantage. It must demonstrate disciplined asset-liability management and lending practices capable of withstanding an economic slowdown.
Singapore’s monetary framework introduces an additional distinction.
In its October 2026 monetary policy statement, the Monetary Authority of Singapore maintained the prevailing appreciation path of the Singapore dollar nominal effective exchange rate policy band.
Unlike central banks that primarily conduct monetary policy by announcing domestic policy interest-rate targets, Singapore manages monetary conditions chiefly through its exchange rate.
Consequently, changes in interest rates in the United States, Australia and Singapore should not be interpreted as identical policy signals.
For households, interest-rate movements affect far more than bank dividends. They influence mortgage repayments, savings returns and everyday cash flow.
For small and medium-sized enterprises, borrowing costs can determine whether an investment project is financially viable.
If banks continually raise lending charges to defend short-term profitability, they risk damaging valuable long-term customer relationships.
If they relax credit standards excessively in pursuit of market share, the eventual risks may prove even greater.
The challenge is therefore not simply to maximise interest income, but to preserve a lending model that remains profitable, competitive and responsible throughout the economic cycle.
The Third Test: Can the Wealth-Management Boom Deliver Lasting Value?
Singapore’s position as an international wealth-management centre provides its domestic banks with a considerable structural advantage.
Affluent families, cross-border businesses and institutional investors frequently require services involving multiple currencies, payments, financing and asset allocation.
Relationships of this kind are strategically more valuable than the sale of any single banking product.
Nevertheless, growth in assets under management does not guarantee an equivalent increase in fee income every quarter.
Customers may increase their deposits while reducing investment transactions. Wealth-management divisions may continue attracting fresh assets even as difficult market conditions temporarily slow revenue growth.
Financial institutions must also absorb the costs of regulatory compliance, cybersecurity, anti-money-laundering controls and assessments of investment product suitability.
A business model’s profitability will be overstated if analysts calculate the revenue generated by clients without accounting for the resources required to protect them.
Singapore Exchange data indicated that some wealth-management and fee-related measures at the three major banks reached record levels, even as overall non-interest income declined significantly.
This distinction matters.
The development of an international financial centre is a long-term undertaking. Its progress will not necessarily be reflected in uninterrupted quarterly earnings growth.
The most valuable banks are not merely those capable of attracting new customers. They are institutions that convince those customers their assets, privacy and financial rights will be treated with seriousness and care.
That confidence cannot be manufactured through marketing campaigns or quarterly earnings announcements. It must be demonstrated through conduct, transparency and resilience.
The Fourth Test: Digital Convenience Must Not Transfer Every Risk to Customers
Competition among modern banks is no longer determined primarily by branch networks and lending rates.
Mobile applications, instant transfers, identity verification, artificial intelligence-assisted services and automated risk monitoring are transforming financial activity.
These technologies improve efficiency. But they also create opportunities for criminals to exploit transaction speed, consumer anxiety and information asymmetries.
According to figures released by the Singapore Police Force for the first half of 2026, Singapore recorded 16,821 scam cases involving approximately S$410.6 million in losses.
Both the number of cases and the amount lost declined compared with the corresponding period a year earlier.
That improvement should be recognised as evidence of progress in combating scams. Nevertheless, the remaining financial damage is substantial.
Particularly significant is the finding that more than 80 per cent of reported cases involved victims who were deceived into initiating the transfers themselves.
A scam does not necessarily require criminals to break into a bank account or defeat an institution’s security infrastructure.
Fraudsters can instead manipulate human behaviour, persuading customers to authorise transactions voluntarily.
This creates a difficult policy dilemma.
Financial institutions have a responsibility to protect their customers, but banks cannot indiscriminately block every legitimate payment.
Excessively restrictive controls can disrupt ordinary transactions, entrepreneurial activity and access to essential financial services, particularly for vulnerable groups.
Yet allowing high-risk transactions to proceed without meaningful safeguards can expose victims to the loss of a lifetime’s savings within moments.
The Monetary Authority of Singapore’s guidance on combating scams explains the Shared Responsibility Framework, which applies to certain phishing scams and establishes obligations for relevant financial institutions and telecommunications companies.
An important distinction must be maintained: the framework has a defined scope. It does not provide automatic compensation for every scam-related loss.
Presenting the policy as a blanket promise that banks must reimburse anyone who has been deceived would create dangerously misleading expectations.
The real challenge is to design a system in which preventive responsibility is shared appropriately, legitimate transactions remain accessible, and customers understand both their protections and their obligations.
The Fifth Test: Fighting Financial Crime Must Not Create Financial Exclusion
As banks strengthen customer screening and transaction monitoring, another risk is emerging.
Some individuals may find their accounts restricted or closed, leaving them unable to conduct ordinary financial activities.
Accounts linked to suspicious transactions may require investigation. But prudent financial supervision must also address false positives, transparency and effective avenues for redress.
In a written parliamentary reply dated November 3, the Monetary Authority of Singapore explained that local banks could offer basic banking accounts with restricted functionality to certain Singapore citizens and permanent residents who had been denied account opening or had their accounts closed, subject to limited exceptional circumstances.
The arrangement attempts to reconcile two legitimate objectives: combating financial crime and preserving access to essential payment services.
This approach deserves recognition, but it also requires continuing scrutiny.
The inclusiveness of a financial centre should not be measured solely by its ability to provide sophisticated products to high-net-worth individuals.
It must also be judged by whether ordinary people can obtain safe, reasonable and accessible banking services, together with meaningful opportunities to appeal decisions affecting their accounts.
Every anti-scam measure should be assessed against the principle of proportionality.
Is the restriction necessary? Could a less intrusive alternative achieve the same objective? When mistakes occur, who is responsible for correcting them?
Anti-scam legislation passed in Singapore in 2026 expanded the powers available to relevant authorities and institutions in specified circumstances.
The effectiveness of such measures should not be evaluated merely by counting the number of accounts restricted.
A more meaningful assessment would consider how much financial loss was prevented, how many legitimate customers were adversely affected, and whether appeals and remedies work in practice.
Financial security should not become a justification for excluding people from the very system intended to protect them.
The Sixth Test: Will Artificial Intelligence Make Banks Safer—or Scams More Convincing?
Artificial intelligence can help banks identify suspicious behaviour. It can also enable criminals to produce increasingly convincing messages, images and impersonations.
The net effect of the technology does not depend on which side adopts the language of AI first.
It depends on the practical quality of data, model monitoring, human review and collaboration across institutions.
In remarks delivered during the Monetary Authority of Singapore’s annual report media conference in July 2026, the authority emphasised the need for banks to strengthen scam-detection capabilities and assess the effectiveness of artificial intelligence in relevant systems.
The report also disclosed that approximately S$47 billion was protected by Money Lock as of May 2026.
Such measures demonstrate an important principle: some friction in financial technology can serve the public interest.
An additional few minutes of verification before a high-risk transfer may be more valuable than an entirely frictionless payment experience.
A joint operation involving the Singapore Police Force and five partner banks between July and August 2026 used automated information processing to disrupt more than 400 scam attempts and prevent over S$46 million in potential losses.
The distinction between potential losses and recovered money is critical.
Preventing a transaction from resulting in a loss is not the same as recovering funds that have already been stolen.
Similarly, freezing suspicious assets does not necessarily mean those funds have been returned to their rightful owners.
Credible financial reporting must distinguish among losses prevented, funds frozen and money actually recovered.
These are different measures of success, and confusing them can distort public understanding of the effectiveness of anti-fraud initiatives.
The Counterargument: Making Banks Responsible for Too Much Can Also Harm Consumers
Criticising banks for insufficient customer protection does not mean every risk associated with financial fraud should be transferred to them.
In many transactions, banks possess only part of the relevant information.
Interactions between customers and third-party platforms often occur entirely outside the banking system.
If regulators required banks to provide full compensation for every payment voluntarily authorised by a customer, institutions might respond by increasing fees, tightening transaction restrictions or reducing services to customers considered high-risk.
These concerns are not merely theoretical.
In a November 4 parliamentary reply concerning safeguards against authorised fraudulent payments, the Monetary Authority of Singapore outlined existing bank protections, including real-time detection, transaction alerts and emergency account-freezing tools.
It also indicated that safeguards would remain under review.
Prudent regulation should reward effective prevention rather than focus exclusively on assigning liability after losses occur.
Yet this counterargument must not become an excuse for financial institutions to disclaim all responsibility.
Banks control payment infrastructure, possess extensive risk-related data and benefit commercially from the scale and efficiency of instant transactions.
It is therefore reasonable to expect them to strengthen their defences continuously under standards that are proportionate, transparent and appropriately targeted.
Such responsibility forms part of the broader social contract between financial institutions and the societies they serve.
Looking Ahead to 2027: Three Scenarios That Could Shape the Industry’s Reputation
Singapore’s banking industry faces three possible trajectories, each carrying different implications for profitability, resilience and public confidence.
Scenario One: Resilient Modernisation
In the first scenario, lending and deposit businesses continue to expand, wealth management develops steadily, and banks gradually improve system security and customer experience.
Profit growth may normalise rather than accelerate dramatically.
Nevertheless, consistent service and effective customer protection could strengthen long-term trust.
This would be the trajectory most consistent with Singapore’s enduring interests as an international financial centre.
Scenario Two: Profits Above All Else
Under the second scenario, intense competition and shareholder pressure encourage financial institutions to place disproportionate emphasis on short-term cost control.
Investment in technological infrastructure, customer protection and employee training receives insufficient attention.
Near-term returns may appear attractive.
But a single serious technological failure or crisis of confidence could erase the benefits of years of operational and financial progress.
Scenario Three: Excessive Defensiveness
The third scenario involves an increasingly restrictive environment in which regulation and internal risk controls create additional barriers to ordinary banking activity.
Scam losses may decline, but false positives, complicated procedures and financial exclusion become more widespread.
Consumers may gain protection against losing their money while simultaneously losing the convenience and freedom to use it.
Such an outcome would hardly represent an ideal financial system.
Future banking policy should therefore examine more than capital adequacy ratios, non-performing loans and earnings growth.
It should also consider scam-related losses, complaint resolution, equitable access to financial services, responses to technological failures and the social costs of anti-fraud restrictions.
Not all these indicators can be reduced to a single financial measure.
Together, however, they reveal something more fundamental: the true quality of a financial system.
Conclusion: Trust Is a Bank’s Most Valuable Capital
Bank share prices rise and fall. Interest rates change. Wealth-management booms inevitably experience cycles.
Singapore cannot guarantee that every investor will always be satisfied. Nor should preventing adjustments in market valuations become an objective of financial policy.
What the country can preserve over the long term is something more consequential: prudent supervision, fair rules and public confidence in the financial system.
The challenges confronting banks today extend far beyond the income statement.
Customers need payment services that are secure without becoming unnecessarily restrictive.
Businesses need continued access to reasonable financing.
Investors require risks they can understand and assess.
Regulators must protect the integrity and stability of the financial system.
If any one of these priorities is neglected over an extended period, the strength of the others may gradually erode.
Singapore’s most important competitive advantage in banking is therefore not the number of financial records its three largest banks can break each quarter.
It is whether those institutions can continue demonstrating that they deserve the public’s confidence amid market volatility, technological disruption and financial crime.
Profit is the outcome of banking activity. Trust is the foundation that allows the financial system to exist.
Frequently Asked Questions
Which are Singapore’s three largest local banking groups?
DBS Group, Oversea-Chinese Banking Corporation (OCBC) and United Overseas Bank (UOB).
Does a decline in bank share prices indicate a crisis in deposit safety?
Not necessarily. Share valuations must be assessed separately from banks’ operational performance, capital strength and overall financial condition.
Are banks required to compensate customers for every scam-related loss?
No. Singapore’s Shared Responsibility Framework covers specific qualifying scams and applies according to defined responsibilities and eligibility requirements.
Discover more from The Economy
Subscribe to get the latest posts sent to your email.


Energy security in 2026 means more than having enough oil in storage. It means sustaining affordable, reliable power and fuel through geopolitical disruption, extreme weather and a rapid rise in electricity demand. The economic consequences reach from factories and transport fleets to inflation, fiscal budgets and national competitiveness. Energy resilience has become a central part of macroeconomic policy.
The International Energy Agency’s October 2026 Oil Market Report describes severe pressure on the diesel market following disruptions to supplies and refining. On October 15, the IEA Governing Board noted that approximately 330 million barrels had been released under coordinated emergency action, with further releases planned. These figures show the scale of the response, not evidence that the supply system has returned to normal.
Key takeaways
- Diesel availability and refining capacity matter as much as headline crude-oil prices.
- High energy costs affect inflation, trade competitiveness, employment and government finances.
- Diversified supplies, efficiency and a reliable grid work together; no single technology guarantees security.
- Emergency inventories buy time but do not replace durable investment in energy systems.
- Pakistan’s priority is to reduce import exposure and electricity-system inefficiency without imposing unsustainable subsidy bills.
Why an oil-price headline is not enough
News coverage often reduces energy markets to a single crude-oil benchmark. Households and businesses, however, buy gasoline, diesel, electricity, gas and heating fuels. Those products depend on refining capacity, transport, storage and local distribution. A country can have access to crude yet face a shortage of a specific refined product.
The IEA’s October report described diesel exports in September running 700,000 barrels a day below the year-earlier level, with declines from Russia and the Middle East only partly offset elsewhere. It also warned that tight diesel markets could extend into 2027 despite an expected recovery in refinery operations. These are forecast conditions, not guaranteed future shortages in every country.
Why diesel? It powers freight, buses, agriculture, backup generation and parts of industry. A bottleneck therefore raises the cost of moving and producing goods even in economies where motorists primarily notice gasoline prices. A slower delivery network can become a food-price and manufacturing problem.
Five layers of energy security
| Layer | Failure mode | Example policy response |
|---|---|---|
| Supply access | Fuel imports or production disrupted | Supplier and route diversification |
| Conversion | Refineries or generation cannot meet need | Maintenance, compatible capacity and flexibility |
| Transportation | Shipping chokepoint or network outage | Alternative routes, storage and grid reinforcement |
| Affordability | Prices exceed household or firm capacity | Targeted relief and efficiency |
| Sustainability | System depends on costly or vulnerable assets | Long-term efficiency and diversified generation |
Original analytical framework; optimal combinations vary by geography.
The layers interact. Strategic inventories are of limited use if fuel cannot reach the point of consumption. Large generation capacity may not prevent blackouts when transmission and distribution fail. Even abundant energy can undermine economic performance if tariffs are unpredictable or hidden public subsidies exhaust budget capacity.
Strait of Hormuz and the limits of emergency reserves
The 2026 disruption to energy flows through the Strait of Hormuz demonstrated how a single maritime route can affect multiple regions. The IEA’s October statement referred to collective action initiated in March and plans to accelerate remaining releases, including diesel. Strategic stocks can smooth the immediate shock and prevent panic buying, but they are finite.
A strategic stock programme works best alongside transparent triggers, monitoring, logistics planning and a strategy for replenishment. Governments that release stocks without a credible replacement plan may reduce current price pressure at the expense of future readiness. Conversely, withholding supplies during a severe shortage can increase the economic cost of interruption. Decisions should be based on severity and duration, not politics alone.
This also illustrates why demand-side options matter. If some activities can shift timing, improve fuel efficiency or use alternative energy sources, the same available supply can support more essential economic activity. Conservation is not merely an environmental appeal during a disruption; it can be a supply-security instrument.
Asia’s rising exposure
Southeast Asia is a useful example because economic growth, urbanization and electrification are simultaneously increasing energy demand. The IEA’s 2026 ASEAN Energy Security Review highlights imported oil and LNG exposure, maritime chokepoints, electricity reliability, clean-energy minerals and regional cooperation. The IEA expects electricity demand in the region to rise around 5.4% annually during 2026–2030 under the report’s projection.
The scale of growth creates a planning challenge. More power stations are not sufficient if grids, storage, demand response and equipment maintenance lag behind. Policymakers must protect reliability while accommodating new demand from industry, cooling and data centres. Fuel choices should reflect local resources, realistic network conditions and whole-system costs.
The IEA’s Southeast Asia Energy Outlook 2026 provides longer-term context for this tension. Some countries can rely on domestic resources for portions of their needs; others depend on international fuel trade. Regional cooperation can improve resilience, but shared networks require transparent rules and investment in cross-border infrastructure.
The electricity problem inside the AI boom
Artificial intelligence is increasing demand for computing infrastructure, which requires steady electricity. The IEA’s October 14 report on powering AI assesses the challenge of integrating data centres without undermining affordability, sustainability or reliability. Power capacity cannot be created by financial investment announcements alone.
There are at least three economic questions. Who pays for the new grid connection and network upgrade? How quickly can additional supply be delivered? What happens if data-centre demand is lower than originally forecast? Poor contracts can leave utilities and their customers with stranded assets. Better contracts allocate capital and demand risk to parties able to manage them.
For developing economies, the opportunity is conditional. A technology facility can anchor skilled work and high-quality connectivity, but it should not crowd out factories and households through exclusive access to cheap or subsidized electricity. The economic test is broad productivity, not the count of data-centre announcements.
Pakistan’s three energy challenges
The import bill. Higher world prices for oil and refined products can strain foreign-exchange needs. Currency movements, shipping and taxation alter the final local cost. Avoiding a narrow focus on one benchmark helps explain why domestic prices may move differently from international crude prices.
The electricity system. Transmission losses, collection problems, costly generation and contract design can influence tariffs and reliability. The IMF’s October Pakistan assessment calls for energy-sector efficiency, cost-reducing reforms and prevention of renewed circular debt accumulation. A supply emergency should not become a justification for avoiding operational reform.
Household affordability. When prices rise, protection is needed for vulnerable consumers. The dilemma is designing support that does not encourage excess use or transfer most resources to high-volume consumers. The IMF October World Economic Outlook argues that temporary targeted transfers can be substantially more cost-efficient than broad price suppression.
A coherent 2026–2030 strategy
First, measure exposure clearly: fuel import dependency, usable inventories, refinery constraints, grid bottlenecks and financial obligations. Second, diversify the system where economics support it, including domestic resources, renewables, storage, transmission and regional links. Third, improve efficiency in buildings, agriculture, transport and industry so each unit of energy produces greater value.
Fourth, design emergency plans before a shortage. Fifth, ensure tariff structures recover legitimate system costs while protecting essential consumption by vulnerable households. Finally, publish investment appraisal and procurement details to guard against expensive contracts entered under crisis pressure.
The IEA ASEAN review emphasizes diversification, electrification, efficiency and regional preparedness as reinforcing elements. The approach is useful beyond ASEAN because energy-system risks rarely respect borders.
What energy resilience is worth to an economy
The value of resilience is often invisible until a crisis. A fuel reserve can appear costly in a normal year; a reinforced grid may look expensive when electricity flows without interruption. Traditional cost comparisons can underestimate these assets when they ignore the economic losses associated with rare but severe failures. A better appraisal estimates expected interruption costs and measures the reduction provided by each investment.
Consider an industrial exporter reliant on consistent electricity. An outage can damage materials, interrupt production schedules, impose generator costs and delay contractual delivery. Lower tariffs are welcome, but a nominally cheap grid that repeatedly fails may be more expensive to the exporter than a dependable system with transparent cost recovery. The same principle applies to irrigation pumps, refrigerated food chains and hospitals, although the social consequences differ.
The IEA’s October ASEAN electricity analysis expects regional demand to rise around 5.4% a year during 2026–2030. That projection strengthens the case for planning generation, networks and flexibility jointly instead of authorizing capacity in isolated projects. It also creates a timing dilemma: build too slowly and reliability deteriorates; build on exaggerated demand projections and customers may pay for unused assets.
Financing structures matter as much as engineering. Public guarantees for fuel supply, generation or grid investment can create contingent liabilities that are not obvious in a project’s advertised tariff. The IMF’s October financial-stability review emphasizes broader vulnerabilities from leverage and funding structures. Energy planners should publish obligations under contracts and test project economics against both lower demand and higher financing costs.
For Pakistan, a resilience agenda should combine better collection and metering with cost-effective grid investment, more transparent contract terms and measures that reduce consumption per unit of output. A durable policy saves fuel, lowers the impact of external shocks and improves business competitiveness at the same time.
Risks and uncertainties
Conflict conditions and fuel forecasts can change abruptly. The October IEA projection may not capture subsequent attacks, refinery outages or policy decisions. Renewables and storage can improve resilience but need appropriate grids and operational planning; gas and oil infrastructure can provide flexibility but also expose consumers to imports and price volatility. Policy evaluation must include total life-cycle costs, fiscal risks and system reliability rather than endorse a single technology.
Frequently asked questions
What is energy security?
The capacity to maintain reliable, affordable and accessible energy supplies through normal conditions and unexpected disruptions.
Why can diesel be expensive even if crude is available?
Diesel prices depend on refinery output, trade routes, inventories, freight and regional product shortages as well as crude supply.
What did the IEA do in 2026?
It coordinated emergency stock actions in response to the Hormuz crisis; its October board statement reported substantial released volumes and further planned releases.
Do renewable technologies automatically eliminate import risk?
No. They can reduce fuel-import exposure but require grids, equipment, storage or flexibility and, in some cases, imported components.
Why are data centres an energy-security issue?
They increase concentrated electricity demand and can require expensive upgrades, affecting tariffs and grid planning.
What should Pakistan prioritize first?
Lower losses and avoidable costs, dependable distribution, transparent energy procurement, targeted household protection and diversified supply.
Conclusion
Energy security is economic security because almost every productive activity depends on fuel or electricity. The correct response to the 2026 shock is not permanent emergency pricing; it is a system capable of withstanding disruptions without sacrificing affordability or fiscal stability. That requires resilience across supplies, networks, investment and institutions—not a single fuel or a single headline announcement.
Discover more from The Economy
Subscribe to get the latest posts sent to your email.
The reliable “tells” that once let a wary consumer spot a scam call — bad grammar, robotic cadence, obvious accent mismatches — have largely disappeared. In 2026, an AI-generated voice can convincingly clone a real person from as little as three to ten seconds of audio, adapt its script in real time under questioning, and pass through a spoofed number that appears to originate from a legitimate bank fraud line. The result is a category of fraud that has moved from a nuisance to a board-level risk, forcing financial institutions to rewrite verification protocols that have gone essentially unchanged for a decade.
Key Takeaways
- Financial institutions reported a 32% rise in deepfake-related fraud attempts in 2025, with over 10% of banks reporting individual deepfake vishing losses exceeding $1 million per case.
- Fraudsters need as little as 3–10 seconds of audio to clone a voice convincingly, with deepfake audio now achieving over 90% accuracy in mimicking real voices, according to multiple 2026 fraud research compilations.
- Vishing now accounts for over 60% of phishing-related incident response engagements, and in more than 80% of voice phishing attacks, attackers use spoofed caller IDs to make calls appear to originate from legitimate numbers.
- The 2024 Arup case remains the reference incident for enterprise risk: an employee at the UK engineering firm authorized 15 wire transactions totaling $25.6 million after joining a video call featuring convincing real-time deepfakes of the company’s CFO and several executives.
- Verizon’s 2026 Data Breach Investigations Report tracks pretexting (synchronous voice or chat manipulation) at 6% of initial access vectors, with phone-based phishing simulations showing a median click rate roughly 40% higher than email-based simulations.
Why Deepfake Vishing Broke the Old Verification Model
Voice-based identity verification has historically relied on a simple, largely unstated assumption: that a familiar voice, speaking in a familiar and contextually appropriate way, is a reasonably reliable signal of identity. That assumption depended on voice cloning being expensive, technically demanding, and largely confined to research labs and high-budget production environments. That constraint dissolved in 2024 and 2025, as open-source models, real-time inference, and cheap, abundant compute closed the technical gap — reducing the cost of a convincing voice-cloning attack from what industry practitioners describe as a “research lab” undertaking to a “weekend project.”
The critical architectural failure this exposes: any verification process that depends on a human listening to a voice and confirming it “sounds right” can now be defeated by AI, because the voice only needs to be convincing under pressure — not indefinitely, and not against forensic scrutiny, just long enough to complete a transaction.
First-Generation vs. Second-Generation AI Vishing
The evolution of AI voice phishing across 2025 and 2026 illustrates why static defenses have consistently fallen behind:
- First-generation (pre-rendered audio): Attackers scripted a short call, generated the audio in advance, and played it through a SIP gateway. Defenders could reliably defeat this by throwing the call off-script — asking an unexpected question, requesting a callback, or changing the topic — because pre-rendered audio could not adapt.
- Second-generation (real-time inference, 2025–2026): Real-time inference services now synthesize responses inside the call itself, with end-to-end latency low enough to feel like a normal conversation. The off-script defense that worked reliably against first-generation attacks is substantially weaker against a system that can adapt its responses live.
This progression matters directly for bank security protocol design: verification procedures built around the assumption that unpredictable questioning defeats vishing are now defending against a threat model that no longer exists in its original form.
The Arup Case: What $25.6 Million Bought as a Lesson
The 2024 Arup incident remains the most frequently cited case study in 2026 vishing analysis, and for good reason: it demonstrates the failure mode at enterprise scale. An employee at the UK engineering firm joined what appeared to be a routine video conference featuring the company’s CFO and several senior executives — everyone looked right, and everyone sounded right. The employee authorized 15 separate transactions totaling $25.6 million to Hong Kong bank accounts before the fraud was identified. The case has become the reference point specifically because it defeated not just voice verification but visual verification simultaneously, illustrating that multi-channel deepfake attacks — voice plus video plus contextually accurate scripting — represent the frontier threat model banks and enterprises must now defend against, not single-channel voice calls in isolation.
How Banks Are Rewriting Security Protocols in 2026
Several concrete protocol shifts are emerging across financial institutions in response to this threat environment:
- Out-of-band verification as a hard requirement. The consistent recommendation across 2026 fraud research is to verify any high-risk request on a channel the caller does not control — for example, calling back through an independently sourced phone number rather than a number provided during the suspicious call itself, or confirming through a separate app-based channel.
- Behavioral and telephony metadata analysis over voice recognition alone. Since caller identity and voice familiarity are no longer sufficient trust signals in high-risk workflows, leading practitioners now emphasize behavioral detection and telephony metadata analysis — call origination patterns, timing anomalies, SIP routing irregularities — as stronger risk signals than voice identity checks.
- Mandatory delay windows for high-value transfers. Given that wire recall success rates drop sharply after the first six hours following a fraudulent transfer, banks are increasingly building mandatory cooling-off periods for large or unusual transfers specifically to create a window for after-the-fact verification.
- Pre-established fraud team relationships. Practitioner guidance increasingly recommends that businesses establish a relationship with their bank’s fraud team before an incident occurs, since wire recall procedures, session revocation, and credential rotation all move faster when a pre-existing escalation path exists.
- No-blame reporting culture. Because deepfake vishing has higher success rates than traditional email phishing due to its emotional-manipulation component, organizations that punish employees for falling victim risk delayed incident discovery; a no-blame reporting culture surfaces incidents in real time rather than days later.
The Data Gap: Where Awareness Training Is Misallocated
A notable finding from 2026 security awareness research is a significant mismatch between actual risk and training prioritization: while 73% of security leaders prioritize phishing reporting training, only 10% prioritize deepfake recognition training specifically — despite 35% of organizations having already experienced a deepfake incident, according to Gartner’s 2025 AI Risk Management Survey. Phone-based phishing simulations show a median click rate roughly 40% higher than email-based simulations, according to Verizon’s 2026 Data Breach Investigations Report, suggesting that voice-channel vulnerability is measurably higher than email-channel vulnerability even as training investment remains skewed toward the latter.
A Practical Vishing Incident Response Framework
- Pre-written wire recall playbook, covering bank fraud-team contact procedures, session revocation, credential rotation, and forensic capture of call metadata
- Mandatory callback verification through independently sourced contact information for any request involving funds transfer, credential reset, or access changes
- Layered channel verification for high-risk requests — requiring confirmation through at least two independent channels (e.g., a callback plus an internal messaging system confirmation) rather than relying on any single channel, however convincing
- Regular, realistic vishing simulation exercises modeled on actual scenarios (bank fraud alerts, executive impersonation, SaaS support calls) rather than generic phishing awareness content alone, given the roughly 40% higher click-through vulnerability documented on phone-based channels
Frequently Asked Questions
How much audio does it take to clone someone’s voice in 2026?
As little as 3 to 10 seconds of audio is sufficient to produce a convincing voice clone using current AI tools, with resulting deepfake audio achieving over 90% accuracy in mimicking the real voice.
What was the Arup deepfake case?
In 2024, an employee at UK engineering firm Arup authorized 15 wire transactions totaling $25.6 million after joining a video call featuring real-time deepfakes of the company’s CFO and several executives — a case widely cited as the reference incident for enterprise multi-channel deepfake fraud risk.
How are banks defending against AI voice phishing in 2026?
Banks are shifting toward out-of-band verification on channels the caller cannot control, behavioral and telephony metadata analysis instead of voice-identity checks alone, mandatory delay windows for high-value transfers, and pre-established fraud-team relationships to speed wire recalls.
Conclusion
The 2026 vishing threat landscape reflects a broader pattern seen across AI-enabled fraud: the technology did not create a new category of crime so much as it removed the practical constraints — cost, technical skill, adaptability — that previously kept an old category of crime in check. Financial institutions rewriting security protocols around out-of-band verification, behavioral metadata, and multi-channel confirmation are responding to a threat model where “it sounded right” and “it looked right” have both stopped being reliable signals of anything at all.
Discover more from The Economy
Subscribe to get the latest posts sent to your email.
Cyber insurance underwriting was built for a threat model measured in hours: an attacker gains access, explores manually, identifies a target, and hands off to a ransomware operator over a window that averaged more than 8 hours as recently as 2022. That model is now obsolete. Mandiant’s M-Trends 2026 report confirms that the median handoff time between initial access brokers and ransomware operators collapsed to 22 seconds in 2025 — a compression that has forced the cyber insurance industry into one of the fastest coverage redesigns in its history.
Key Takeaways
- Median attacker handoff time collapsed from more than 8 hours in 2022 to 22 seconds in 2025, per Mandiant’s M-Trends 2026 report — faster than any human-staffed security operations center can realistically detect and respond.
- The first confirmed agentic ransomware operation (“JadePuffer”) was disclosed in July 2026, involving an LLM-orchestrated attack that exploited a critical Langflow vulnerability (CVE-2025-3248, CVSS 9.8) to autonomously conduct reconnaissance, credential theft, lateral movement, and encryption of AI artifacts and databases.
- “AI & Emerging Technology Liability” is the fastest-growing new cyber insurance coverage category in 2026, with insurers increasingly asking about AI governance and unbundling AI-specific risk from standard policies at renewal.
- Global cyber insurance premiums are forecast to rise 15–20% in 2026, reversing a recent decline, driven by a 47% surge in initial ransomware demands in 2025 and an 800% increase in infostealer-driven credential theft over a similar period.
- Average ransomware payments now exceed $400,000 in 2026, with total event cost (ransom, recovery, business interruption, and legal) reaching $1M–$5M for mid-size businesses — and 27% of data breach claims face exclusions leading to partial or zero payouts.
The 22-Second Benchmark: Why It Changes Everything
The scale of the shift documented in M-Trends 2026 is difficult to overstate. In 2022, the gap between an initial access broker establishing a foothold and handing that access off to a ransomware operator averaged more than 8 hours — a window that, while tight, at least theoretically allowed a well-staffed security operations center to detect anomalous activity, investigate, and respond before catastrophic damage occurred. By 2025, that median window had collapsed to 22 seconds.
The operational sequence behind this compression, as documented by threat researchers tracking agentic AI attacks, looks roughly like this:
- Second 0: Agentic AI agent gains initial access (credential theft, phishing)
- Second 4: Agent autonomously maps the network environment
- Second 11: Agent identifies the highest-value lateral movement target
- Second 22: Access is handed off; secondary payload is deployed
No human-staffed security operations center can meaningfully respond to an attack that completes within that window. This single fact is reshaping both cybersecurity defense architecture and cyber insurance underwriting simultaneously.
JadePuffer: The First Confirmed Agentic Ransomware Case
In early July 2026, cloud security firm Sysdig disclosed what researchers describe as the first documented, fully agentic ransomware operation, tracked as JadePuffer. The threat actor exploited CVE-2025-3248 — a critical missing-authentication vulnerability (CVSS score 9.8) in Langflow, a Python-based, LLM-agnostic open-source framework used for building AI agent workflows — to gain access to an internet-exposed instance. From that foothold, an LLM-driven, largely autonomous process conducted reconnaissance, discovered credentials, moved laterally, and proceeded to encrypt AI model artifacts, training data, and production databases, deleting tables as part of the extortion mechanism.
This case matters specifically for AI cyber liability underwriting because it demonstrates a new category of exposure: AI infrastructure itself — model artifacts, training data, and agent orchestration frameworks — is now a high-value, directly targetable asset class, distinct from traditional file servers and databases that legacy cyber policies were designed around.
Why Standard Cyber Policies Are Being Unbundled
Insurance industry analysis in 2026 has identified “AI & Emerging Technology Liability” as the fastest-growing new coverage category, driven by carriers recognizing that standard cyber policies were not actuarially designed for AI-specific loss scenarios. A notable trend documented by insurance agents in 2026: AI coverage is being quietly carved out of standard commercial general liability and cyber bundles at renewal, with new ISO forms treating AI-related exposure as a distinct risk category requiring separate underwriting, separate sublimits, and often separate premium calculation.
Carriers in 2026 increasingly require, as baseline conditions for any cyber policy:
- Multi-factor authentication (MFA) across all privileged access points
- Endpoint detection and response (EDR) or extended detection and response (XDR)
- Offline, immutable backups
- Documented AI governance frameworks covering model access, agent permissions, and audit logging
Organizations with weak controls in these areas face either coverage denial or premiums 3–5 times higher than well-controlled peers.
The Pricing Picture: What 2026 Premiums Actually Look Like
| Business Size | 2026 Typical Annual Premium | Coverage Limit |
|---|---|---|
| Small business | $750–$5,000 | Often $1M aggregate |
| Mid-size company ($5M–$10M revenue) | $3,500–$15,000+ (varies by industry) | $1M–$5M aggregate |
| Large enterprise | $75,000–$350,000+ | Varies significantly |
S&P Global Ratings has forecast a 15–20% premium increase across 2026, reversing a brief recent decline, citing three converging pressures: successful attacks now cost roughly 17% more per incident than in 2024, ransomware incidents rose 126% in Q1 2025 alone, and infostealer-driven credential theft surged 800% over a comparable period. Global cyber insurance premiums, which rose roughly 7% in 2025 to approximately $15.3 billion, are forecast by some analysts to double by 2030, with other projections putting the market at roughly $29 billion by 2027.
Coverage Gaps Businesses Should Scrutinize
Several structural coverage gaps recur across 2026 cyber policies and warrant specific attention during renewal negotiations:
- Social engineering / funds transfer fraud sublimits. Most policies include only a modest sublimit — commonly $100,000 — for this category by default, even though real-world losses from business email compromise and voice-based fraud regularly exceed $50,000–$300,000 per event and can run far higher.
- AI-related exclusions. As AI liability is unbundled into its own coverage category, businesses relying on legacy cyber policies purchased before this shift may find AI-related incidents — including agentic ransomware events like JadePuffer — explicitly excluded from coverage.
- Ransom payment exclusions tied to sanctioned entities. With 86% of businesses refusing to pay ransom in 2025 (a record high, per Coalition’s 2026 Cyber Claims Report), sanctions-related payment restrictions are increasingly relevant to claims outcomes even for businesses willing to pay.
- 27% of data breach claims face exclusions leading to partial or zero payouts, according to NAIC-referenced data — underscoring that policy language review, not just premium comparison, should drive purchasing decisions.
A Practical Underwriting Checklist for 2026
- Confirm whether AI/agentic-AI incidents are explicitly included or excluded under the current policy language, not assumed to be covered under general “cyber incident” definitions
- Verify MFA, EDR/XDR, and offline backup requirements are met and documented, since these increasingly function as coverage preconditions rather than discount qualifiers
- Increase social engineering and funds transfer fraud sublimits beyond default levels given real-world loss data
- Request telemetry-based or on-site underwriting assessment rather than relying solely on self-reported security questionnaires, which security researchers note frequently produce unreliable risk pricing
Frequently Asked Questions
What is the “22-second ransomware” threat?
It refers to Mandiant’s M-Trends 2026 finding that the median handoff time between initial access brokers and ransomware operators has collapsed to 22 seconds, down from more than 8 hours in 2022, driven by agentic AI tools that autonomously conduct reconnaissance and lateral movement.
Does standard cyber insurance cover AI-related ransomware attacks?
Increasingly, no — by default. “AI & Emerging Technology Liability” is being unbundled into its own coverage category in 2026, meaning businesses should explicitly verify whether agentic AI incidents are covered rather than assuming standard cyber policies apply.
How much does cyber liability insurance cost in 2026?
Small businesses typically pay $750–$5,000 annually, mid-size companies $3,500–$15,000+, and large enterprises $75,000–$350,000+, with premiums broadly forecast to rise 15–20% in 2026.
Conclusion
The compression of ransomware attack timelines from hours to 22 seconds represents a genuine inflection point, not incremental threat evolution — and the insurance industry’s rapid unbundling of AI liability coverage in 2026 is a direct, rational response to that shift. Businesses that treat cyber insurance renewal as a routine annual exercise, without specifically confirming AI-related coverage and reviewing sublimits against current loss data, are carrying risk exposure that their policies were never actuarially designed to cover.
Discover more from The Economy
Subscribe to get the latest posts sent to your email.

Oil Shocks and Core Inflation: Why the Two Move Differently

Singapore Cannot Fight Financial Fraud by Making Victims Bear the Risk Alone

Singapore Banking’s Real Test: Beyond Profits, Who Will Safeguard Financial Trust?

Nvidia’s Share Price Is Not a Scorecard for Singapore’s AI Future

The Australian Dollar Is Not Asia’s Oracle. Singapore Should Listen Anyway

Singapore’s Bank Sell-Off Is Really a Test of What Stability Is Worth

Why a Weaker Currency Makes Imported Food More Expensive

How Oil Price Shocks Raise Food Prices in Importing Countries

Petrol and Diesel Prices in Pakistan Today: Complete Update for 9 November 2026

Wall Street’s Renminbi Paradox: Banks, Beijing and the Dollar

The Market Economy Is Winning

Bitcoin’s Dollar Trap: The Chart That Exposes the Future of Money

Dow Jones Today: Dow Slips 237 Points After the Worst Day Since April 2025

Australia’s AI-Driven Economic Strategy Is Redefining National Resilience

Social Security Extra $90 Deposit: Who Qualifies for the October 2026 Medicare Rebate?

Stock Market Crash in 2026? Warning Signs, Scenarios and a Calm Investor Checklist

US–Iran Conflict in October 2026: Hormuz, Oil Prices and Diplomacy
Dow Jones Today: Dow Slips 237 Points After the Worst Day Since April 2025

China’s AI Microdrama Boom: How Beijing Is Reshaping Global Media

SSI November 2026 Payment: Why Benefits Arrive October 30

US–China AI Export Controls in 2026: Chips, Testing Rules and Corporate Risk

Pakistan IMF Programme 2026: Why Bailouts Keep Returning

2027 Federal Tax Brackets: New IRS Rates and Standard Deductions Explained

EU-China Trade Deal 2026: How Beijing and Brussels Avoided a Trade War—and Who Wins

Q3 2026 Earnings Preview: Can Record Profit Expectations Keep Wall Street’s Rally Alive?

Stock Market Crash 2026? What the November Rout Actually Tells Us

KSE-100 Index 2026: Is Pakistan’s Stock-Market Recovery Sustainable?

Singapore Stock Market Outlook 2027: The STI’s Bank-and-Yield Test
-

 Markets & Finance10 months ago
Top 15 Stocks for Investment in 2026 in PSX: Your Complete Guide to Pakistan’s Best Investment Opportunities
-

 Analysis9 months ago
Johor’s Investment Boom: The Hidden Costs Behind Malaysia’s Most Ambitious Economic Surge
-

 Analysis9 months ago
Top 10 Stocks for Investment in PSX for Quick Returns in 2026
-

 Banks10 months ago
Best Investments in Pakistan 2026: Top 10 Low-Price Shares and Long-Term Picks for the PSX
-

 Analysis9 months ago
Brazil’s Rare Earth Race: US, EU, and China Compete for Critical Minerals as Tensions Rise
-

 Investment10 months ago
Top 10 Mutual Fund Managers in Pakistan for Investment in 2026: A Comprehensive Guide for Optimal Returns
-

 Global Economy11 months ago
15 Most Lucrative Sectors for Investment in Pakistan: A 2025 Data-Driven Analysis
-

 Global Economy11 months ago
Pakistan’s Export Goldmine: 10 Game-Changing Markets Where Pakistani Businesses Are Winning Big in 2025